Claude Security 迎来重大更新:支持持续扫描、漏洞修复跟踪及 MCP 集成
英文标题:ArticleOct 21, 2026Claude Security now scans continuously and tracks fixesClaude Security now keeps up with your repositories as code changes, tracks findings until they’re fixed, learns from the context your team adds, and connects to your tools through an API and MCP. Available in public beta for Claude Enterprise customers.Claude Security
Anthropic 宣布旗下 Claude Security 面向 Claude Enterprise 客户推出全新公测版本,由包括 Claude Mythos 在内的完整模型家族驱动。该版本引入了持续代码监控机制,可随代码提交动态扫描并自动追踪漏洞修复状态,同时支持跨仓库安全分析与基于团队知识库的威胁建模。此外,新版新增了 API、Webhooks 以及面向 Claude.ai 和 Claude Code 的 MCP 连接器,并为企业客户提供每月 25,000 美元的限时免费额度,大幅加速了代码安全漏洞从检测到闭环修复的端到端自动化流程。
 455.7 KB
 497.4 KB
 314.3 KB
 332.9 KB
 46.7 KB
中文
自 Claude Security 于 4 月进入公开测试以来,已有数千家企业与机构使用它发现了超过 100 万个安全漏洞。
Claude Security 现已不再依赖人工手动触发扫描,而是能够随着代码变更实时跟进代码仓库状态,持续跟踪各项漏洞发现的修复进展,并结合团队提供的环境上下文信息来判断风险优先级。Claude Security 由我们全系列的模型驱动(包括 Claude Mythos),且无需 Cyber Verification Program 准入权限。
最新版本的 Claude Security 即日起面向 Claude Enterprise 客户开启公开测试。企业客户每月可获得 25,000 美元的免费使用额度,为期两个月。该优惠适用于截至 2026 年 12 月 31 日前的用量。完整条款可在帮助中心查看。
持续监控,紧跟代码变更
单次扫描只能捕捉特定时刻的状态,而代码每天都在迭代。用户团队向我们反馈,希望获得能够自动保持最新状态的安全防护,无需专人手动安排排期。
创建项目后,你可以通过 Claude GitHub 应用(支持 GitHub Enterprise Server)或 GitLab 等其他 Git 代码托管平台的访问令牌(access token)连接代码仓库,并为每个仓库指定分支与扫描范围。Claude 会先执行一次深度的基线扫描,随后根据风险与复杂度定期扫描增量变更,确保漏洞列表始终贴合代码的最新状态。
单个项目可容纳多个代码仓库,因此 Claude 能够捕获跨服务存在的安全隐患——例如后端误信了本应由客户端进行校验的输入数据。
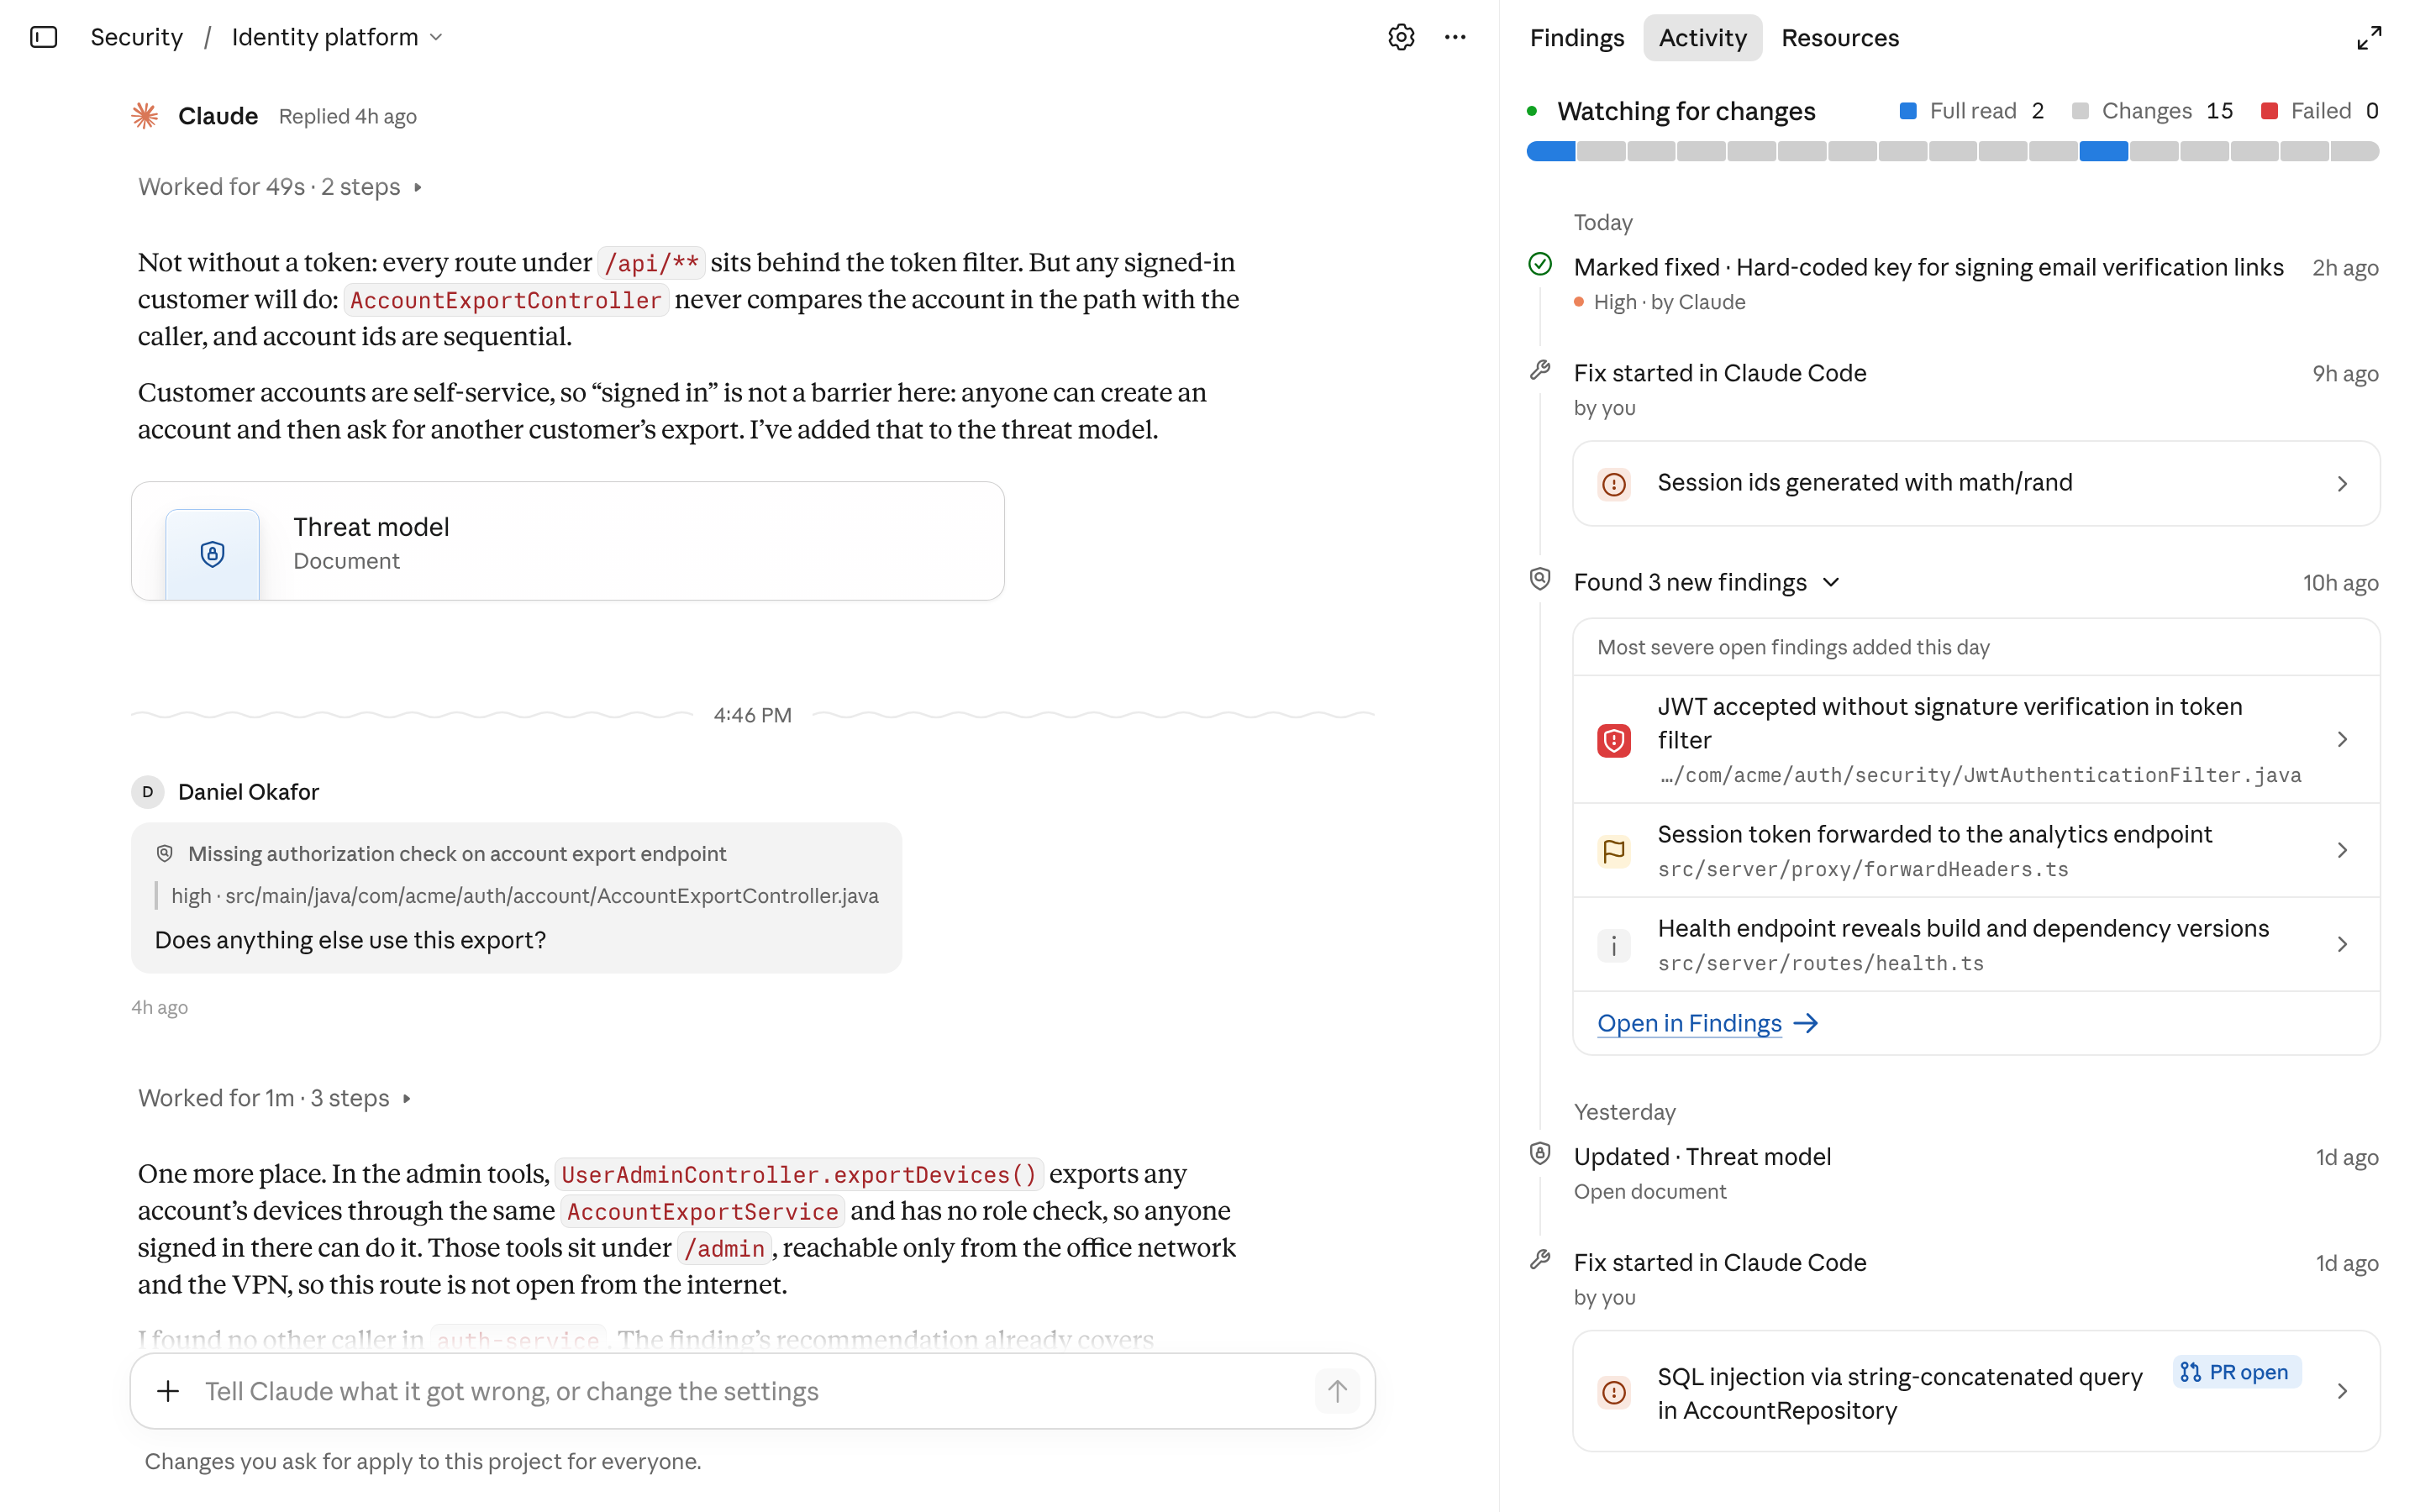
修复上线即自动标记为已解决
大多数漏洞修复都是在发现漏洞的工具之外完成的。Claude Security 会根据变更的代码核对未解决的漏洞,并在修复代码合入时将其标记为已解决,无论团队是在 Claude Code 内部还是在独立流程中完成的修复。如果 Claude Security 稍后再次检测到该问题,则会自动重新打开该漏洞项。
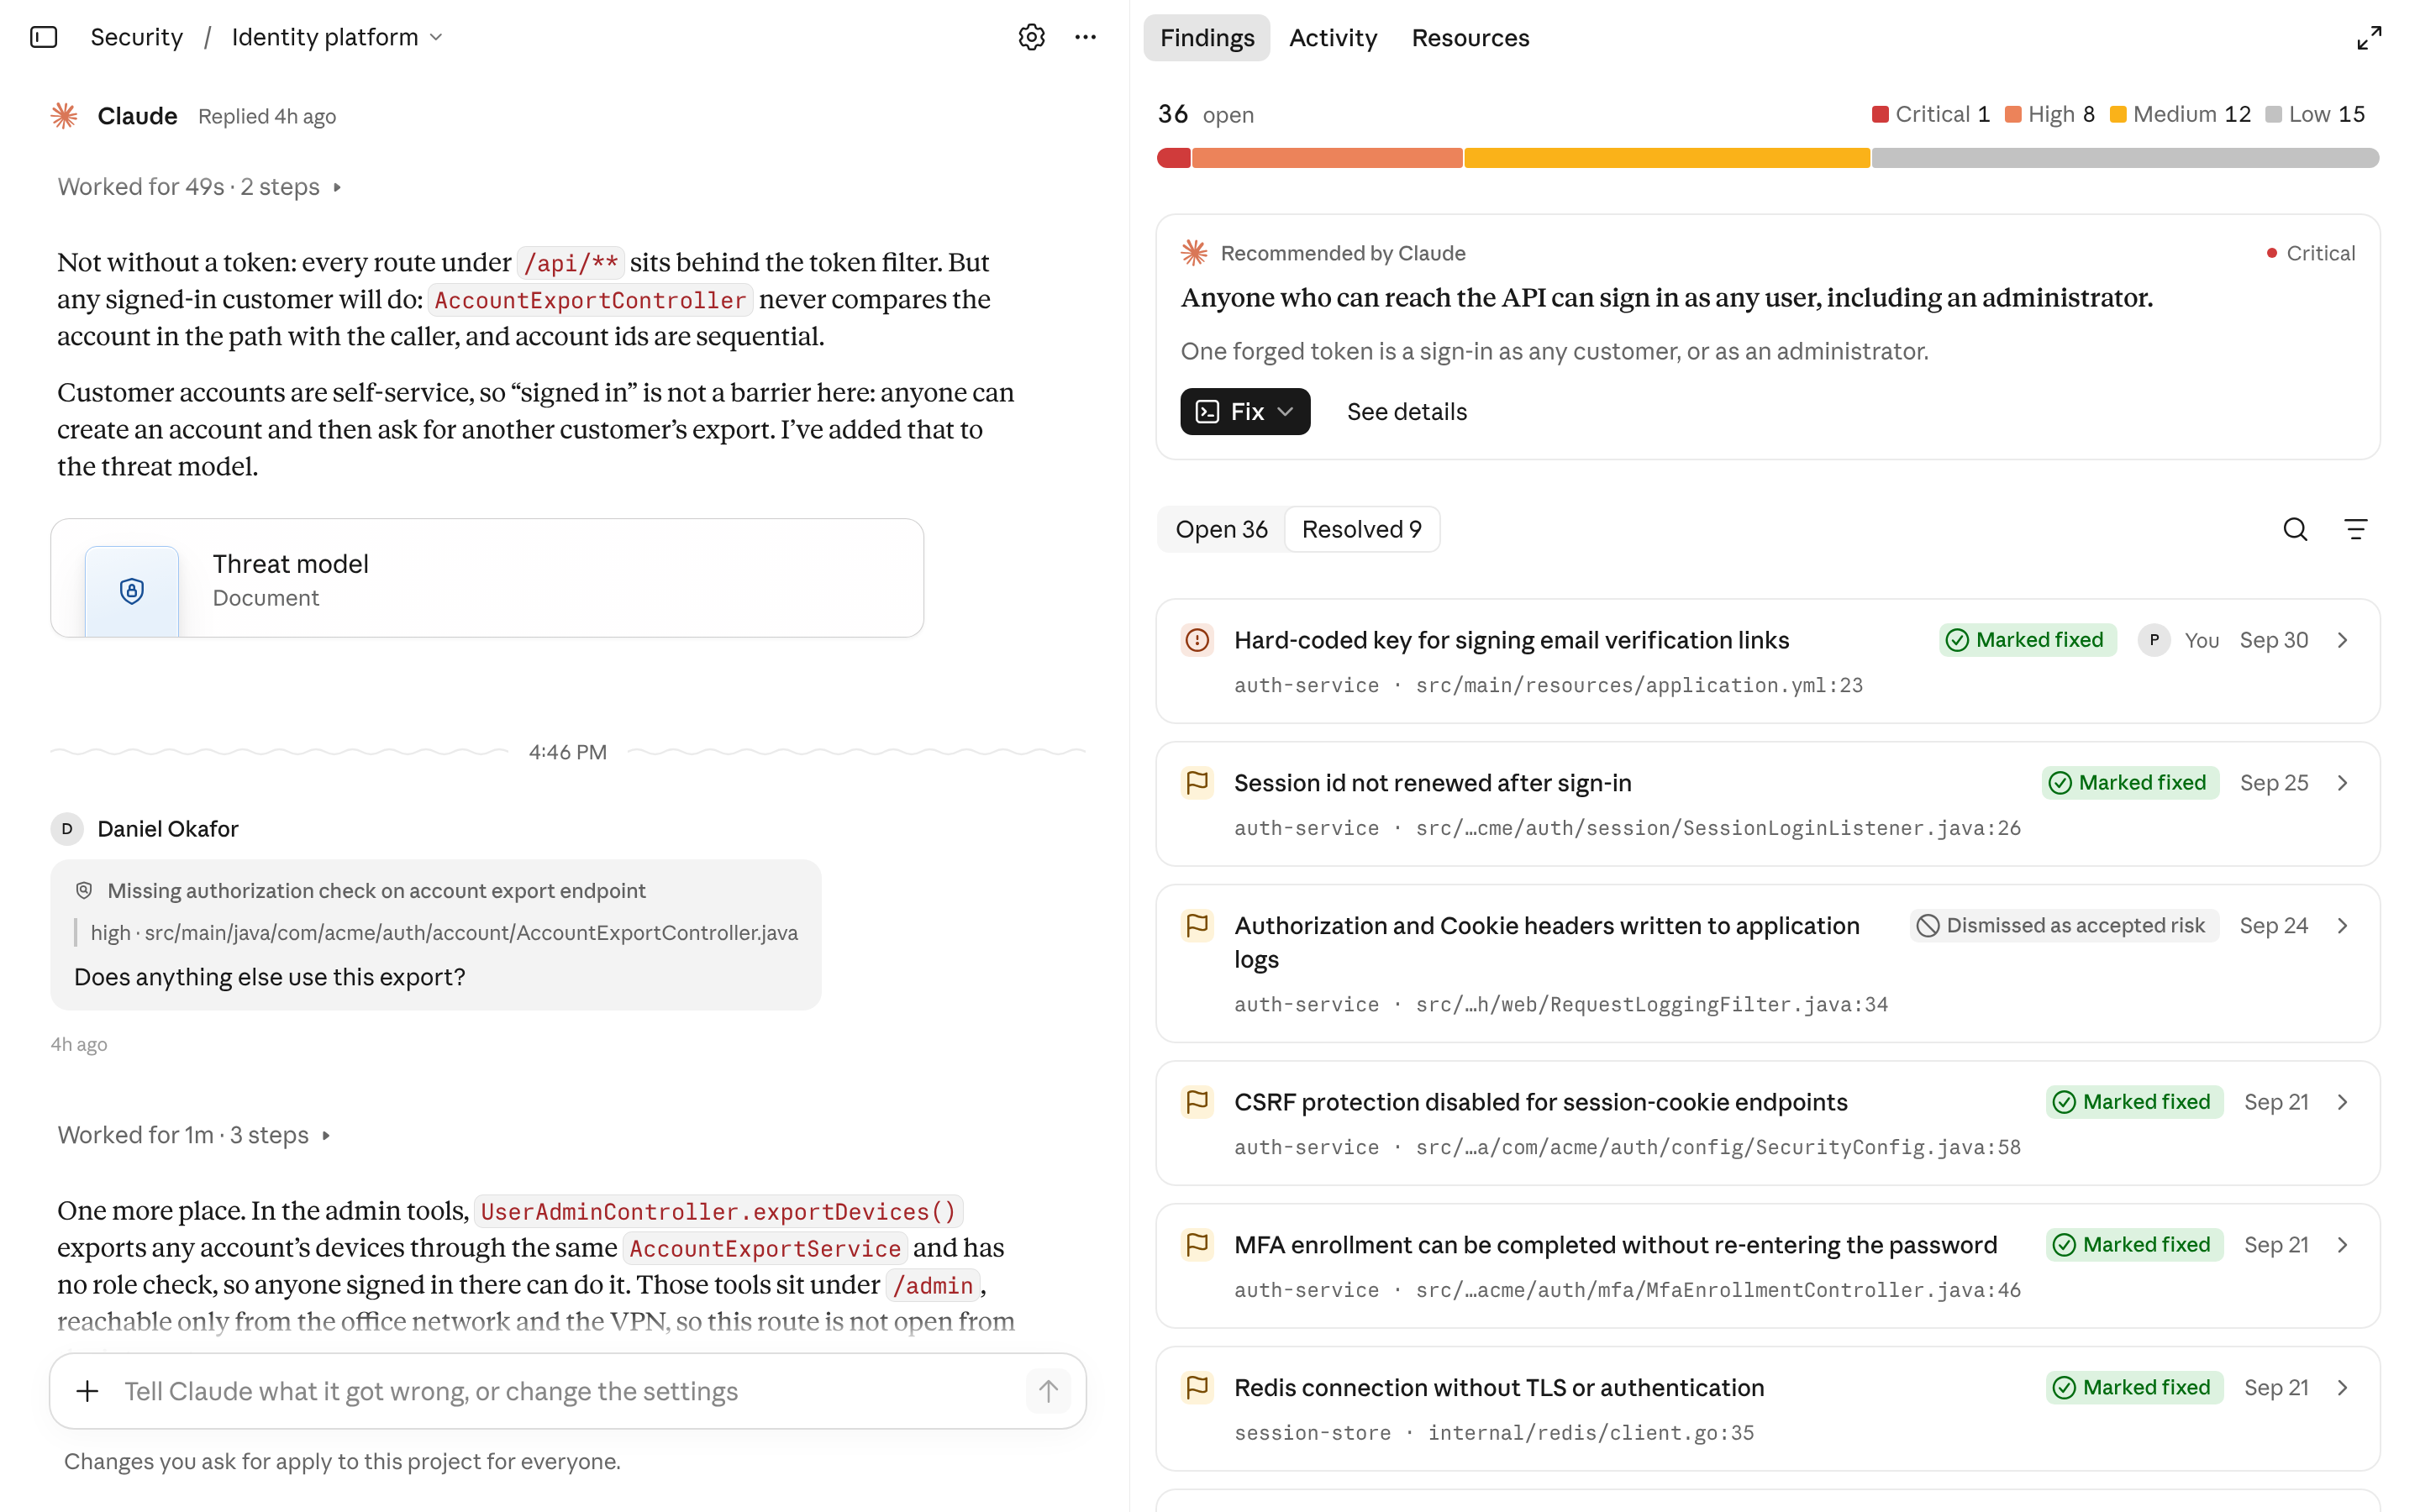
融入团队知识,赋能定制化扫描
每个运行环境都有仅凭代码无法观察到的安全管控措施。各个团队希望有一种方式能将这些管控告知 Claude Security,并支持跨相互依赖的服务进行联合排查。现在,每个项目都配有独立的知识库,你可以在其中说明代码的部署方式、适用的安全策略,以及团队新入职安全工程师需要了解的所有信息。
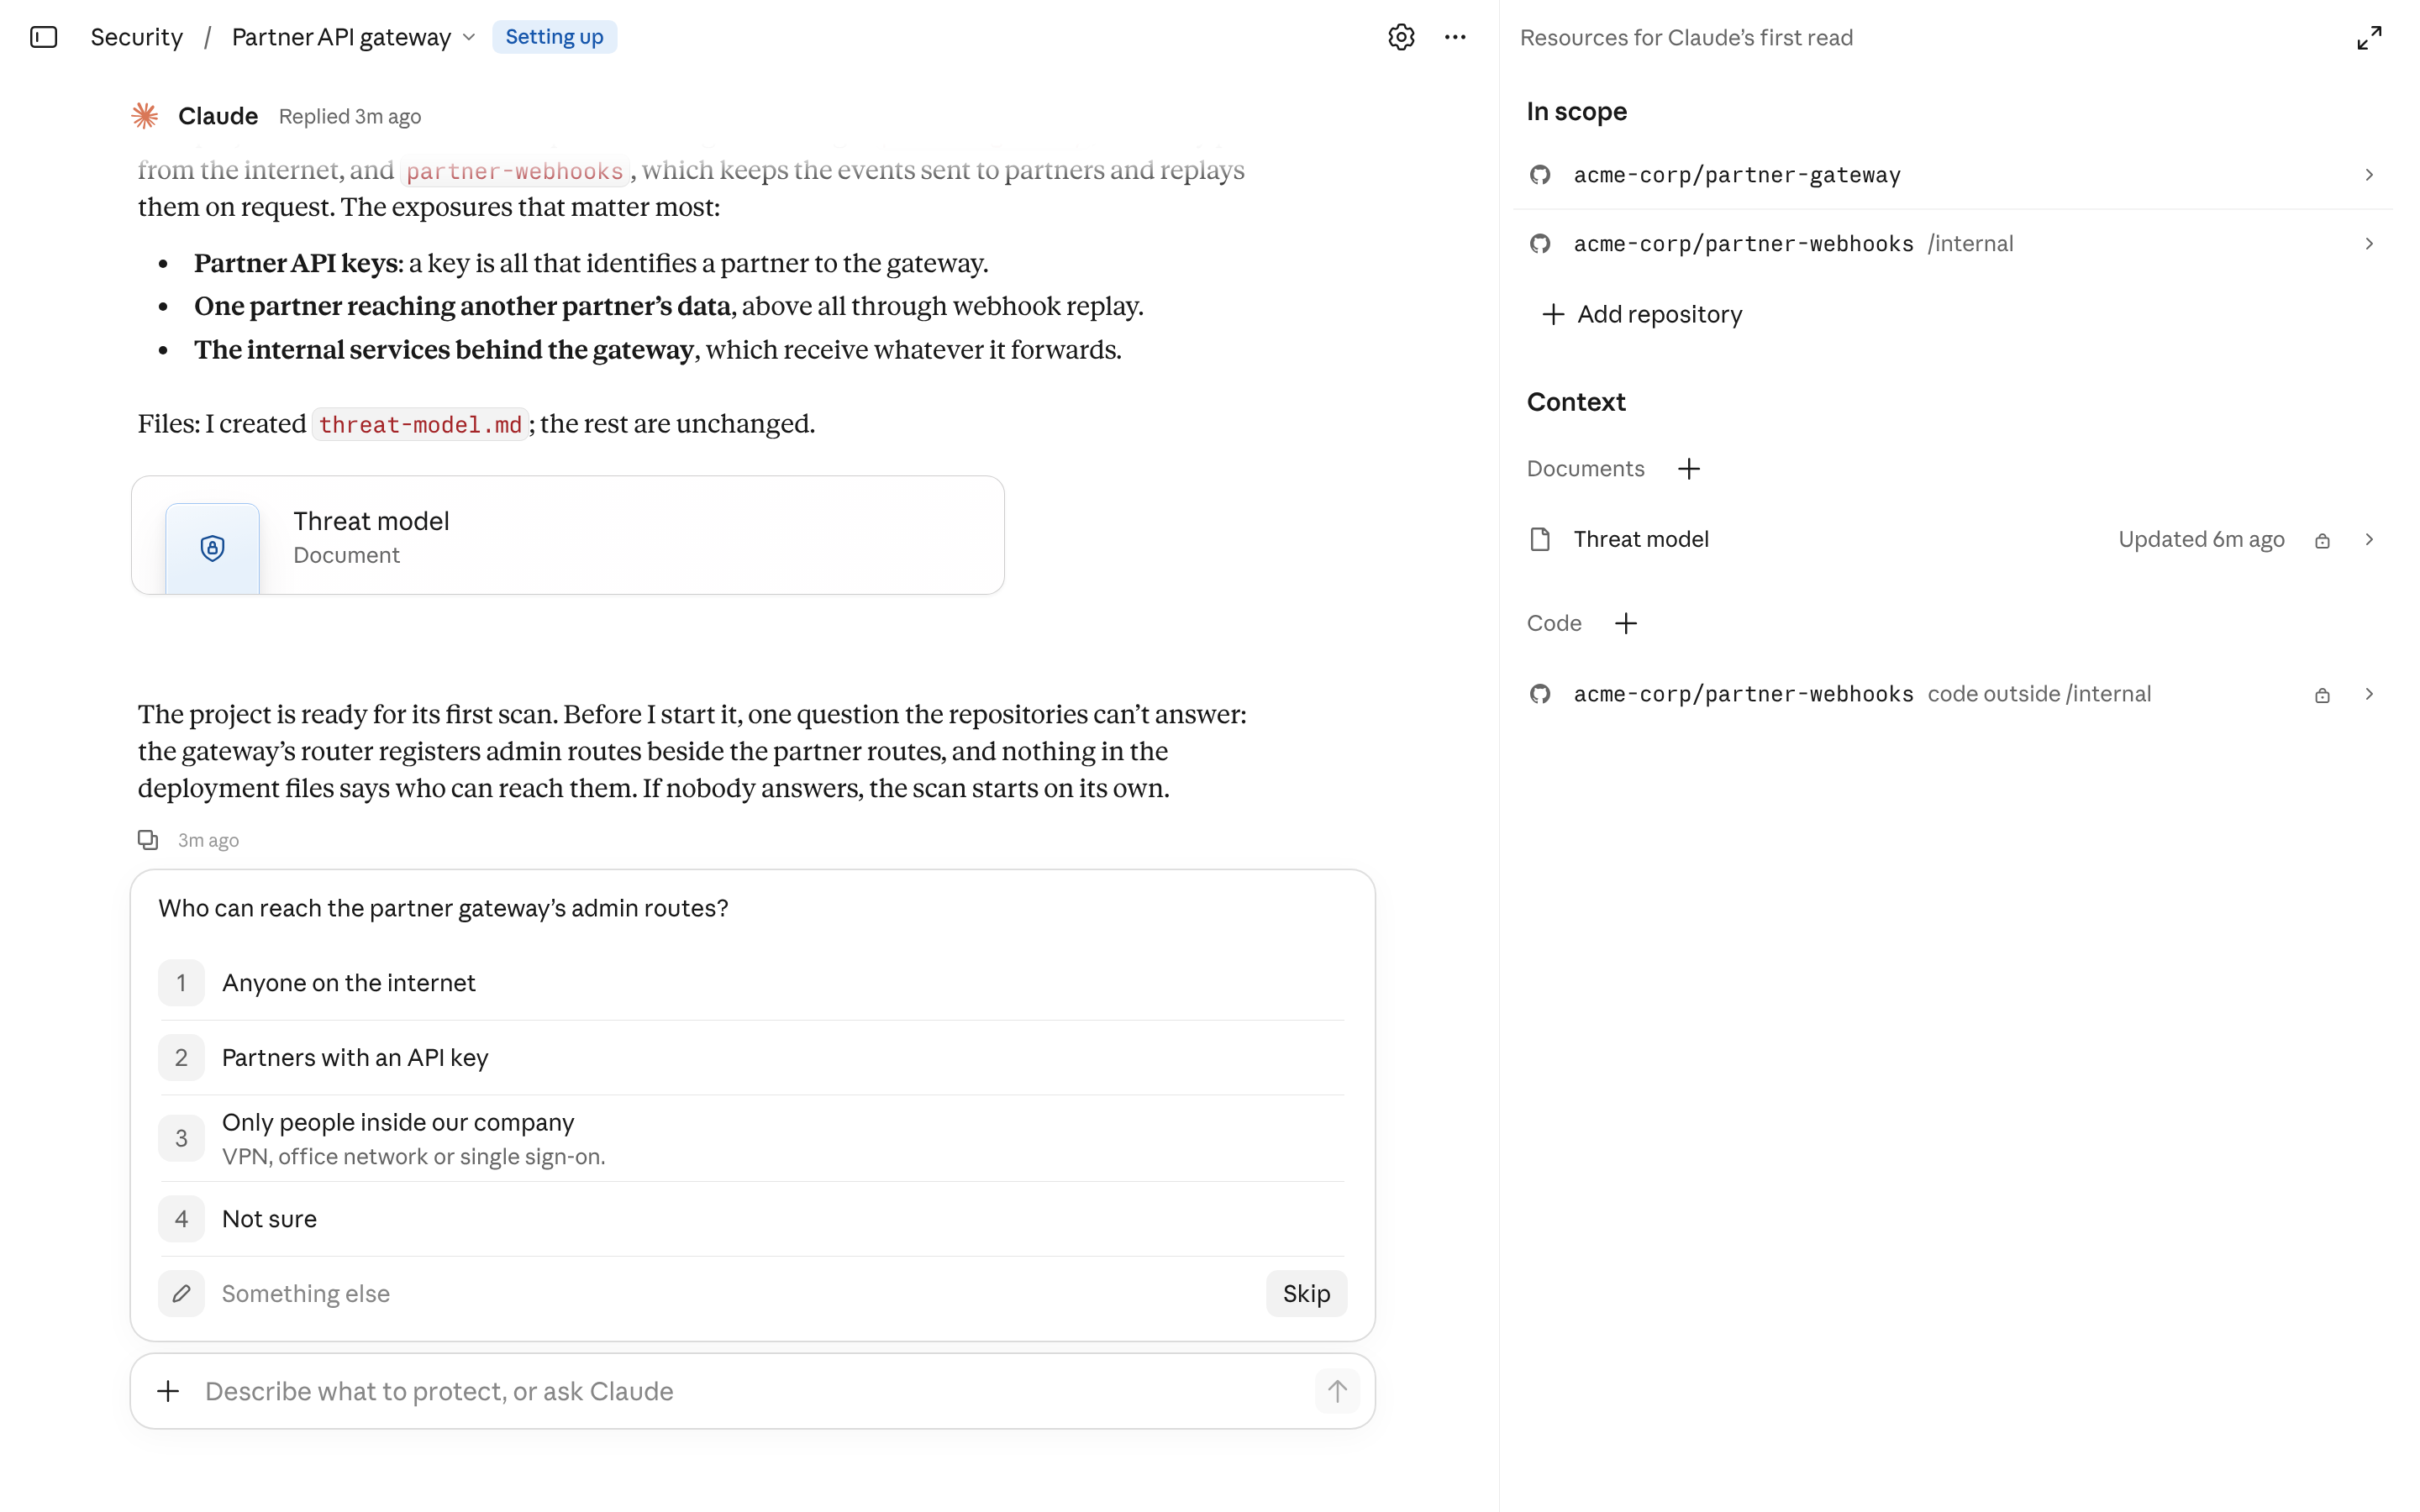
Claude Security 还会根据你的代码自动生成威胁模型,供团队审查与编辑。后续扫描将借助这些威胁模型来评估哪些问题值得预警。补充的上下文信息还能帮助 Claude Security 自动忽略当前环境已妥善处置的潜在风险。
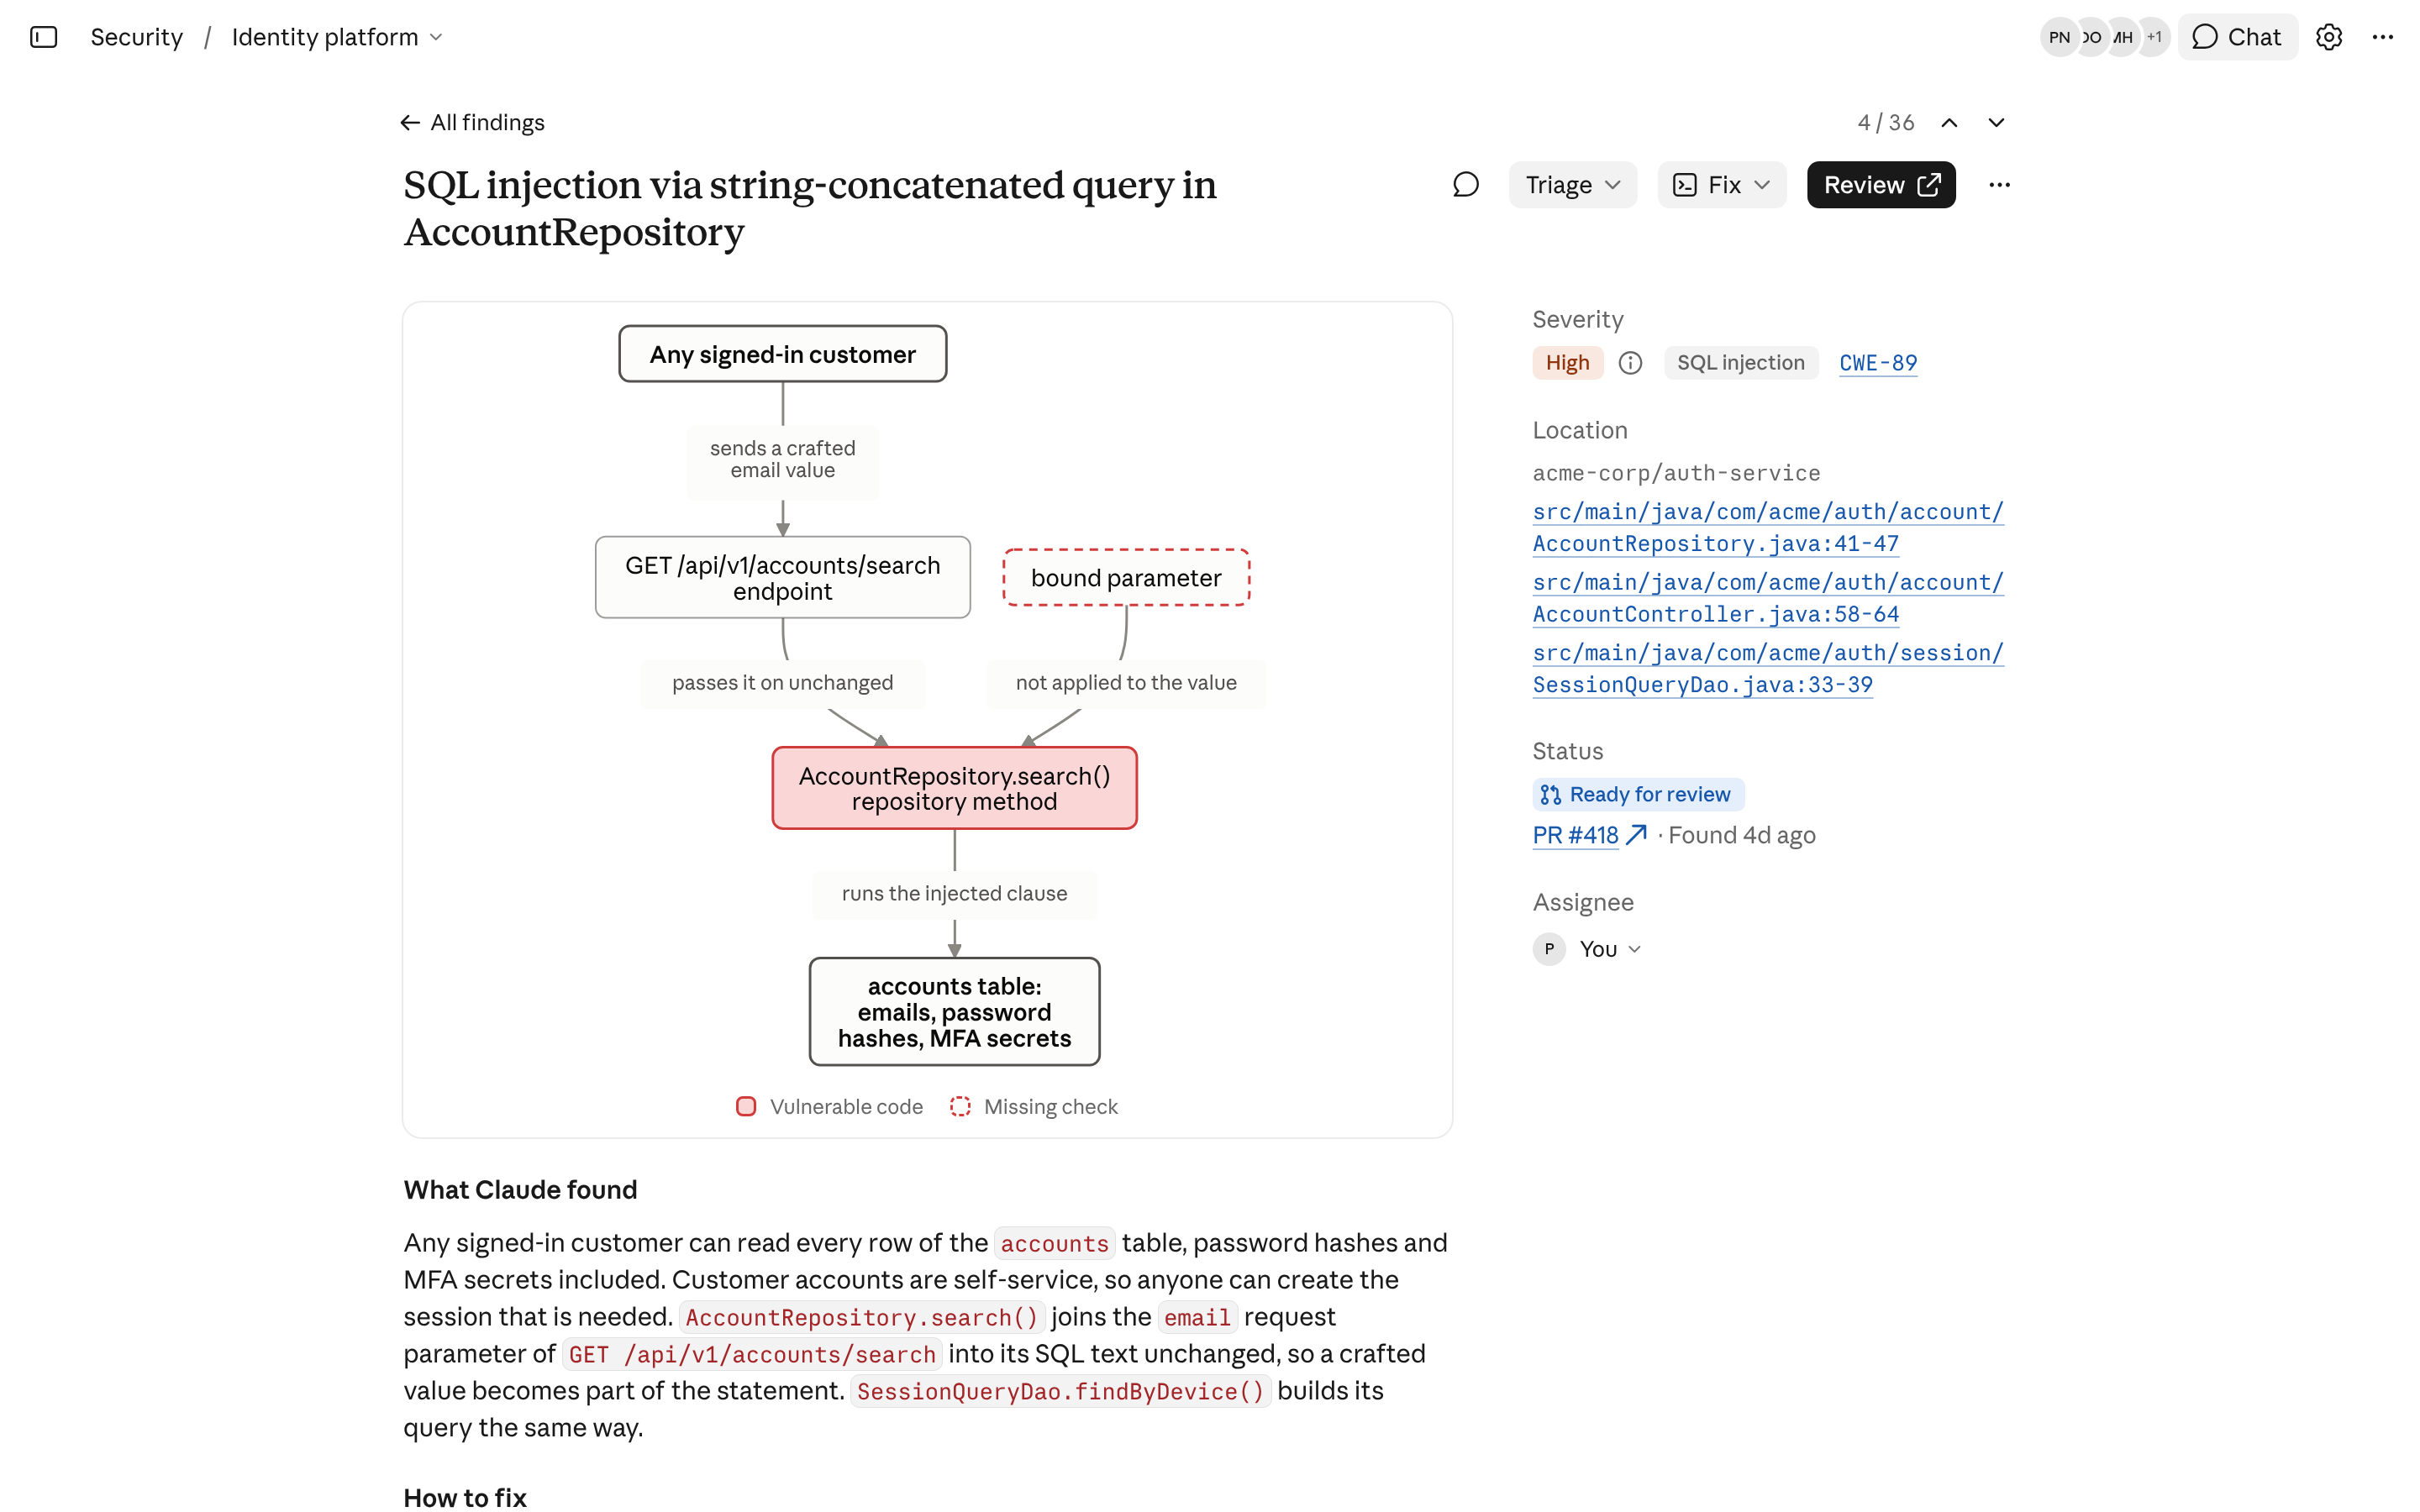
为每个漏洞提供严重程度评估与利用路径
每项漏洞发现均附带根据项目威胁模型评估的严重程度评级,以及攻击者如何触达漏洞代码的详细说明,便于团队优先修复真正具有可利用性的漏洞。漏洞报告中还可包含攻击路径图谱。
全新的 API 支持将 Claude Security 无缝集成到现有的工作流中。你可以查询和读取项目与漏洞详情、标记解决或重新打开漏洞,以及创建和管理项目及其所属仓库。用户可在 Claude Security 设置中生成个人访问令牌(PAT),其权限严格受限于该用户自身的权限范围。此外,Webhooks 还可在新漏洞出现时实时通知外部系统。
Claude Security 现已作为 MCP 连接器集成至 Claude.ai 和 Claude Code 中。工程师可以在同一次会话内调出漏洞详情、向 Claude 咨询相关信息、着手修复并直接标记为已解决。
新增的基于角色的访问控制(RBAC)允许管理员配置谁能查看项目、分流(triage)漏洞以及创建项目。企业可在不向所有人开放项目创建权限的前提下,将 Claude Security 开放给更多负责对应代码的研发团队。
开始使用
最新版本的 Claude Security 即日起面向 Claude Enterprise 客户开启公开测试。管理员可在管理控制台中启用该功能并配置团队成员的访问权限。
欢迎查阅入门指南创建你的首个项目,或访问帮助中心了解更多详情。
企业客户每月可获得 25,000 美元的免费使用额度,为期两个月。该优惠适用于截至 2026 年 12 月 31 日前的用量。完整条款可在帮助中心查看。
English / 原文
Since Claude Security entered public beta in April, thousands of organizations have used it to find over a million vulnerabilities.
Instead of waiting for someone to start a scan, Claude Security now keeps up with your repositories as your code changes, keeps track of which findings get fixed, and uses what your team tells it about your environment to decide what matters. Claude Security is powered by our full family of models, including Claude Mythos, with no Cyber Verification Program access required.
The latest version of Claude Security is available today in public beta for Claude Enterprise customers. Organizations receive $25,000 in free usage credits each month, for two months. The offer applies to usage through December 31, 2026. You can view full terms in the Help Center.
Continuous monitoring keeps up with your code
A scan captures one moment, and code changes every day. Teams told us they wanted coverage that stays current without anyone having to schedule it.
Create a project, connect your repositories through the Claude GitHub app (including GitHub Enterprise Server) or with an access token from GitLab and other Git providers, and choose the branch and scope for each. Claude runs a deep baseline scan, then scans changes regularly based upon their risk and complexity, so your list of findings stays close to the current state of your code.
A project can hold multiple repositories, so Claude can catch issues that live between services, like a backend that trusts input a client was supposed to validate.
Findings are marked fixed when the fix ships
Most fixes happen outside the tool that found the issue. Claude Security checks open findings against the code that changed and marks them fixed when the fix lands, whether your team fixed it in Claude Code or in a separate process. If Claude Security finds the issue again later, the finding reopens automatically.
Your team’s knowledge shapes the scan
Every environment has controls a scanner can’t see from the code alone. Teams wanted a way to tell Claude Security about those controls, and to look across services that depend on each other. Now, each project has a knowledge base where you can describe how your code is deployed, which security policies apply, and anything a new security engineer on your team would need to know.
Claude Security also generates a threat model from your code that your team can review and edit. Subsequent scans use those threat models to decide what’s worth flagging. Added context also helps Claude Security skip risks your environment already handles.
Severity and exploit paths for every finding
Each finding comes with a severity rating, judged against your project’s threat model, and an explanation of how an attacker could reach the vulnerable code, so teams can fix what’s actually reachable first. Findings can include a diagram of the attack path.
The new API lets you integrate Claude Security into your existing workflows. You can list and read projects and findings, resolve or reopen findings, and create and manage projects and their repositories. Users can create a personal access token in Claude Security settings, and it can only see and change what the user can. Webhooks can also notify your systems when a new finding lands.
Claude Security is also available as an MCP connector in Claude.ai and Claude Code. An engineer can pull up a finding, ask Claude about it, start the fix, and mark it resolved in the same session.
New role-based access controls let admins decide who can view projects, triage findings, and create projects. Organizations can open Claude Security to more teams that own the code without giving everyone access to create projects.
Getting started
The latest version of Claude Security is available in public beta for Claude Enterprise customers starting today. Admins can enable it in the admin console and set who on their team can access it.
Use the Getting Started Guide to set up your first project, and visit the Help Center for more details.
Organizations receive $25,000 in free usage credits each month, for two months. The offer applies to usage through December 31, 2026. You can view full terms in theHelp Center.