Claude Duet 的安全、隐私与安全机制详解
英文标题:ArticleOct 23, 2026Claude Duet Safety, Privacy, and SecurityClaude Duet is a proactive agent that works for you, even while you’re away. It builds on two layers of protection: safety training in the Claude model itself and the safeguards that exist in products like Claude Code and Claude Managed Agents. On top of those, we added new protections for working across your accounts and acting on your behalf.
Claude Duet 是一款依托云端环境运行的主动式 Agent,能够在用户离开时持续自主执行跨应用工作流。为防范自主代理带来的隐私泄露和越权风险,Anthropic 确立了三大核心防护机制:引入独立于主模型的敏感信息安全分类器、重要操作强制用户审批,以及从物理与架构层面杜绝 Agent 接触密码、Cookie 和登录 Token。此外,Duet 还整合了独立虚拟机隔离、一次性虚拟卡支付以及严格的自动化意图检查。这套深度防御体系为行业在开发生产级自主 Agent、解决凭据安全与人机协同控制方面提供了关键的技术范式。
 185.8 KB
 199.4 KB
 1.6 MB
 171.7 KB
 149.5 KB
 45.1 KB
中文
Claude Duet 是一款目前处于研究预览阶段(Research Preview)的 Agent,它利用云端计算机为您执行工作。它可以使用您选择接入 Claude 的所有应用程序和服务,即使在您关闭应用后仍能持续运行。在您离开期间,它可以阅读收件箱、拟写回复草稿、预订事项并运行日常例行任务。我们团队在自己的账户上运行 Claude Duet,并在日常工作中广泛使用它。
我们在三项指导 Agent 行为的原则之上构建了 Claude Duet:
- 借助一个在消息发出前自动校验的新分类器,审慎处理您的个人信息以及其他人在您已关联应用中共享的内容。
- 您始终对它代表您执行的操作拥有控制权。
- Claude Duet 绝不会接触到您的密码、浏览器 Cookie、登录 Token 或其他凭据。
Claude Duet 虽然是一项新功能,但其背后的理念早已成型。在 2025 年,我们发布了安全且值得信赖的 Agent 框架,将以人为本的控制权、隐私保护和安全交互视作基本准则。自那以后,我们撰文阐述了为什么单一防御措施并不足够,以及为什么仅靠模型内部的防护无法独立支撑安全。我们还通过 Claude Managed Agents 构建并运营着企业在生产环境中运行 Agent 的基础设施,而 Claude Duet 同样以相同方式将凭据与 Agent 进行物理隔离。它立足于这些前期工作,进一步补充了 Agent 代表您采取行动时所必需的保护机制。本文将详细介绍我们新增的防护措施以及目前仍在推进的工作。
重要操作需由您亲自审批
一个在您离开时执行任务的 Agent,必须明确知道何时应该停下来请求许可,并以恰当的节奏发起确认。在 Claude Duet 执行诸如发送潜在敏感消息、付款或删除任何内容等操作之前,它会向您展示操作类型、目标对象和具体内容(包括所有收件人),然后等待您的批准。
在每项操作执行的同时,系统还会运行独立的自动化检查。该检查基于 Claude Code 的 auto mode 分类器构建,并针对 Claude Duet 进行了扩展。它负责评估该操作是否符合您的真实意图。由于该检查运行在执行任务的模型外部,因此页面中隐藏的恶意指令无法影响检查结果。
部分操作即使获得您的批准也严禁执行,例如证券交易、银行账户间转账等金融操作,以及访问他人的账户。另有一些步骤则完全不受“不再询问”规则的约束——无论您过去批准过多少次,系统每次都会发起确认,比如付款或转账、删除订单或创建新账户。在您离开时运行的例行任务同样受这些防护规则约束。
我们在校准 Claude Duet 请求批准的频率上投入了大量时间。“审批疲劳”是一个严重的问题,因为过多的请求会导致用户不假思索地一键放行,从而失去安全防范意义。随着时间的推移,我们将继续对这一节奏进行动态调整。
在购物支付方面,Claude Duet 会使用来自 Stripe Link 等钱包服务的一次性虚拟卡进行支付,额度仅限于该商家和对应金额。您可以看到商品明细和总额,并在 Link 应用中确认购买。您的真实卡号绝不会透露给 Claude Duet 或商家。
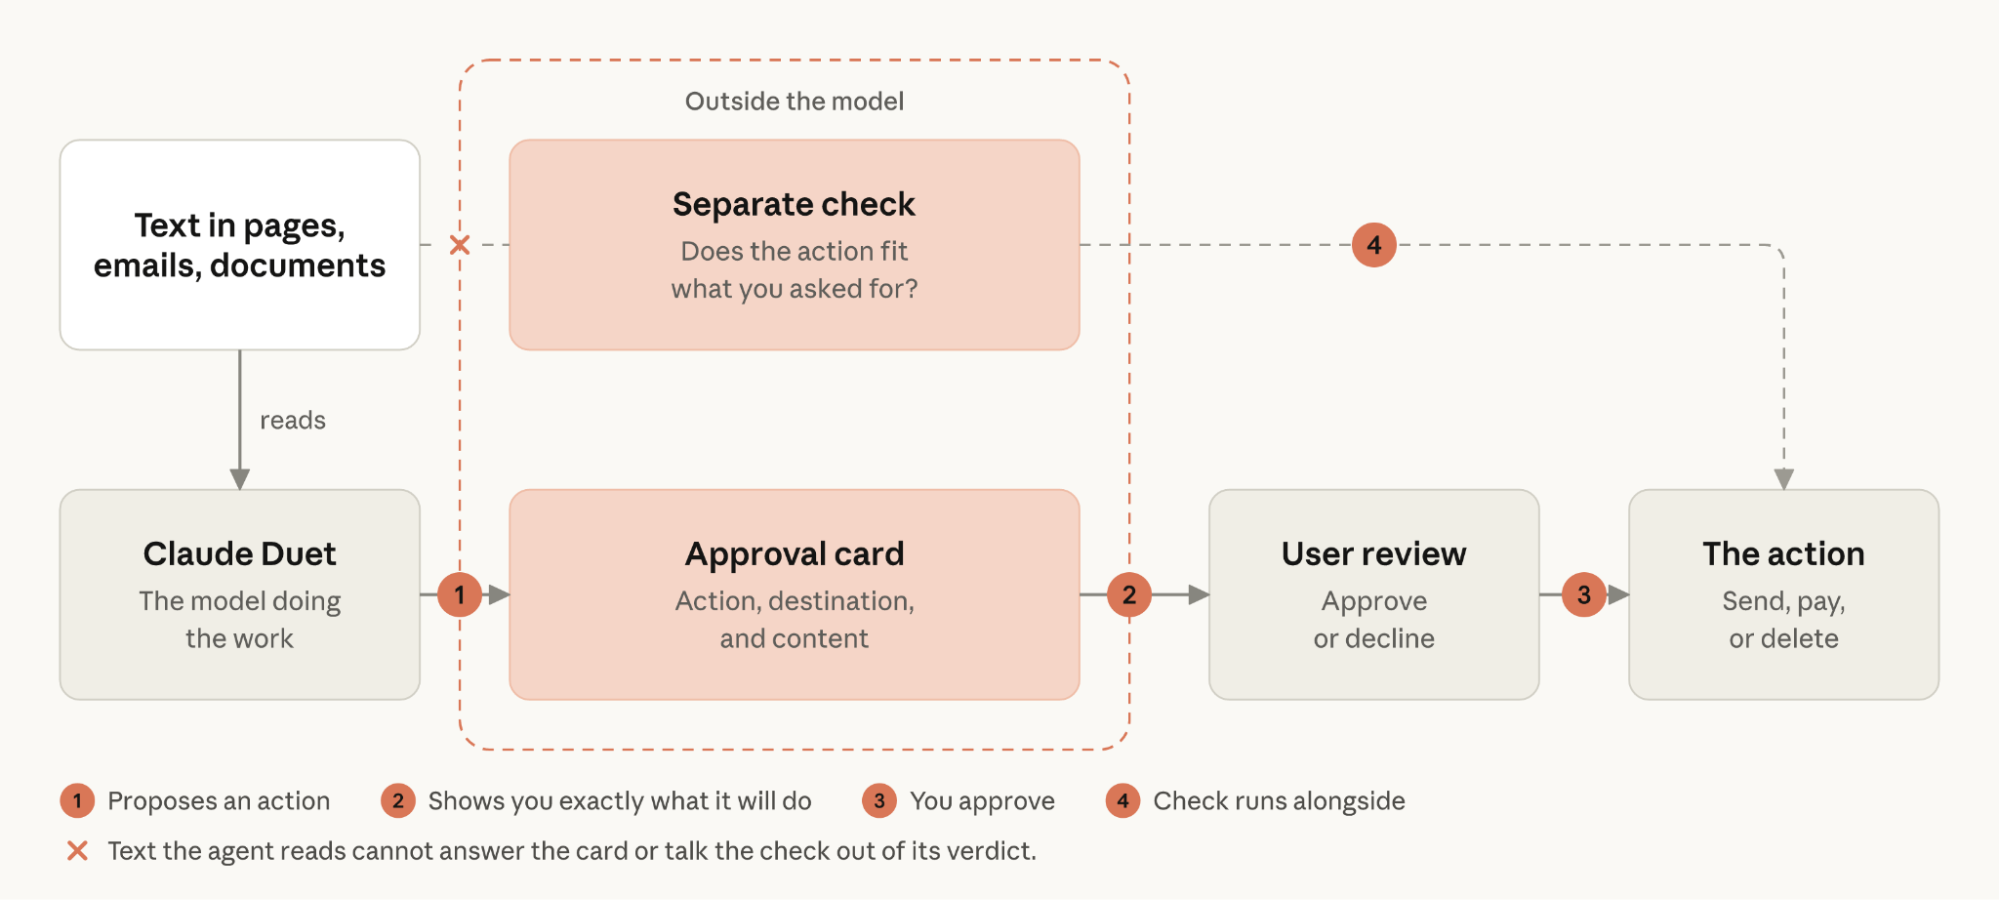 图 1. 审批流程:审批卡片与独立检查机制位于模型外部,因此 Agent 读取的任何内容都无法直接回应或绕过该卡片。
审慎处理您的个人信息
一个能阅读电子邮件并代表您发送消息的 Agent,必须时刻判断不同类型信息的去向与边界。如果您要求 Claude Duet 向团队发送每周总结,它应当仅包含团队成员均有权访问的内容,而绝不能包含私人细节,例如您的绩效评估沟通记录。
为解决这一问题,我们构建了一个独立于主模型运行的全新安全分类器,用于检查 Claude Duet 即将发送的每条消息中是否包含潜在敏感信息。我们将此类信息划分为两个层级:
- 绝不共享(Never share): 我们对登录凭据、完整银行卡号与银行账号、政府身份证件号等信息提供最顶级的保护。Claude Duet 受到严格指令约束,即使您明确要求,也绝不能与任何人共享这些内容。
- 需征得同意方可共享(Needs consent to share): 对于健康状况或财务状况等其他私人信息,只有在获得您明确批准的情况下,Claude Duet 才会共享。您自身发出的指令可直接视为授权,因此像“给我的牙医发信说明牙痛情况”这类请求,通常无需二次额外审批。
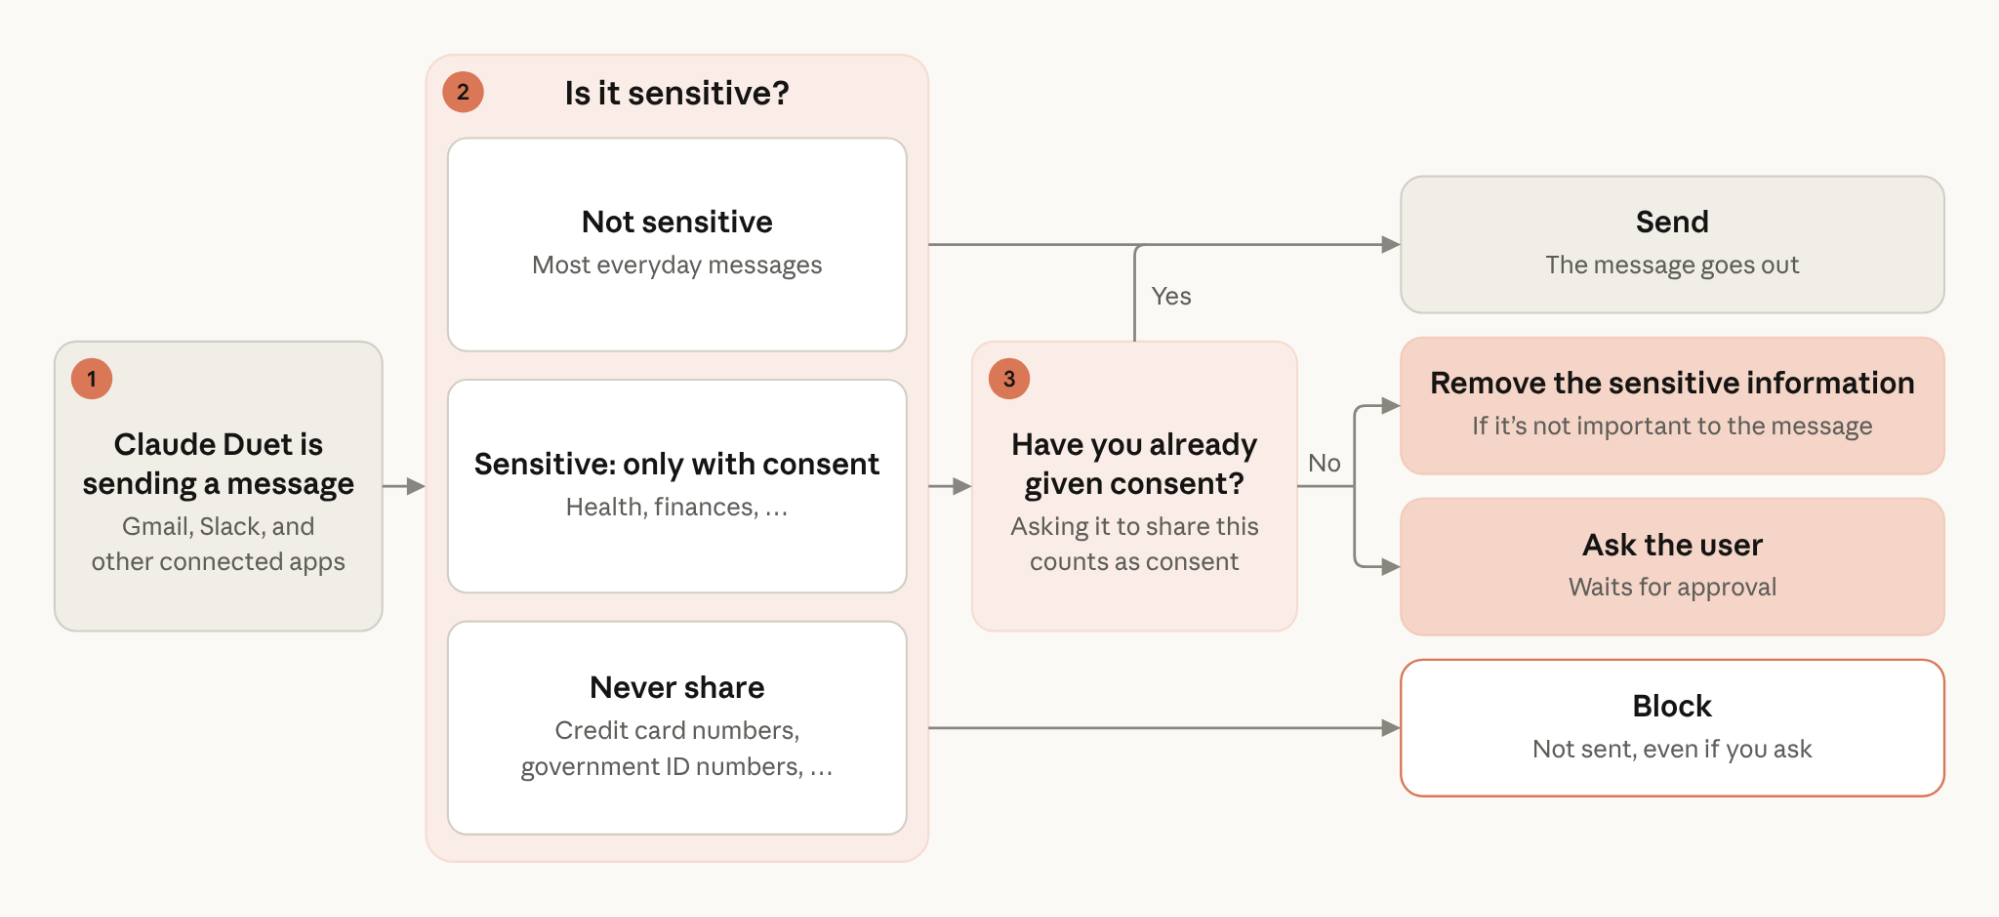 图 2. 信息的流向控制:在发送任何内容之前,检查机制会评估信息的敏感程度以及您是否已给予许可。
如果 Claude Duet 因上述任一原因被拦截,它可以决定重写消息并剔除敏感信息,随后提交给您审批。
Claude Duet 目前仍处于研究预览阶段,这些防护措施偶有遗漏或误判无害信息的情况。这正是它们需要与上述人工审批机制协同工作的原因——二者结合以确保您对 Claude Duet 代表您发送的内容拥有最终决定权。随着我们对用户实际使用方式的深入了解,我们将持续迭代优化该分类器。
任务与关联应用保持高度透明
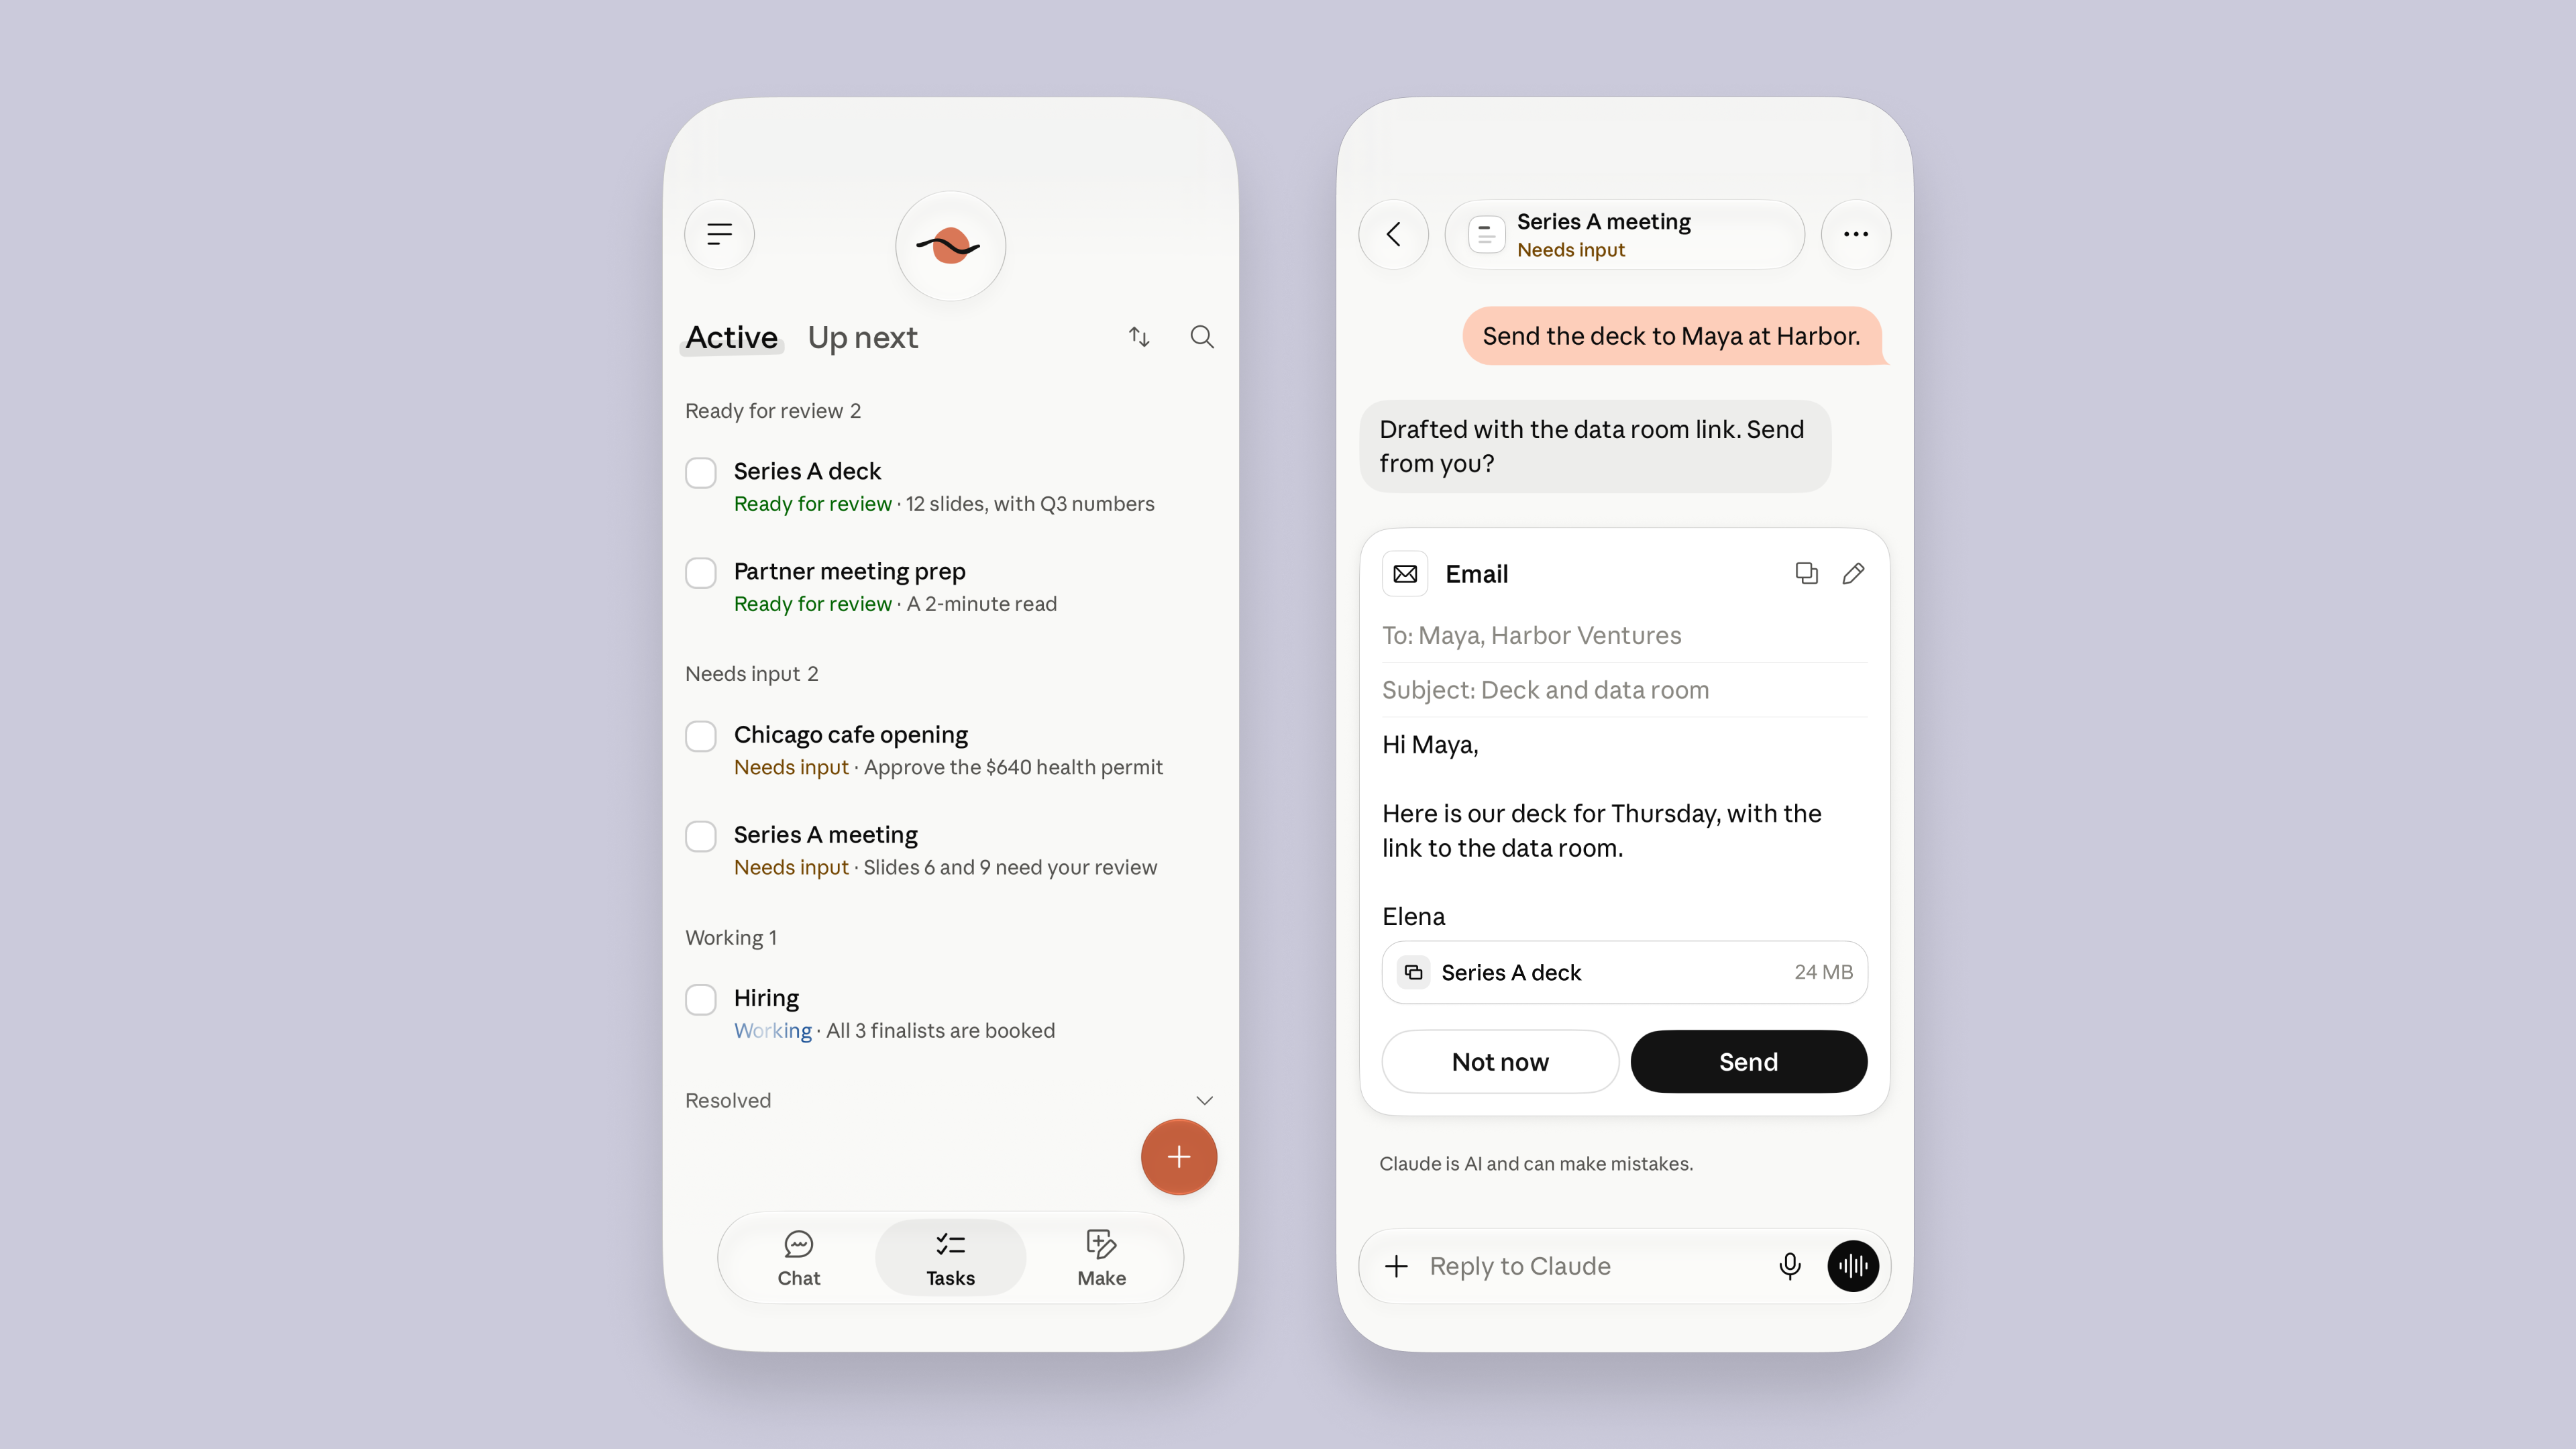
您可以在任务列表中查看 Claude Duet 已经完成以及正在执行的操作,每个任务都有专属页面,您也可以在任务执行中途介入接管。Claude Duet 会保留您的对话历史和记忆,以便在不同任务之间延续上下文,直到您主动删除历史或重置记忆。一旦删除账户,Claude Duet 存储的所有数据都将被彻底清除。
您关联至 Claude 的应用程序会自动同步至 Claude Duet,在任意一处关闭某个应用,该应用在两处都会被停用。断开应用连接会立即终止新的访问权限,但 Claude Duet 此前从中学习到的内容会保留下来,直到您在应用设置中随时重置其记忆。Claude Duet 还会调用您 Claude 账户中的记忆,因此 Claude 从您早期聊天中记住的细节同样对其可见。
凭据与浏览器与模型严格隔离
Claude Duet 绝不会接触到您的密码、浏览器 Cookie 或已连接应用的登录 Token,也无法将它们保存到自身记忆中。这些凭据仅会在模型无法访问的独立计算环境中流转,负责约束其行为的审批机制与安全检查也同样运行在隔离环境中。
密码
当网站需要密码时,您会在 Claude 应用内的表单中输入密码。该表单会使用仅存在于我们安全云端浏览器机器上的单次密钥对密码进行加密,专供该次使用。加密后的密码会在未解密的状态下直接传递给浏览器,由浏览器代填至目标网站。模型无法看到密码,也无法将其保存或复现。很快,您还将支持使用 1Password 登录;Claude Duet 会发起凭据请求,您在 1Password 中批准该请求后,凭据将直接发送给浏览器,全程不经过模型。
由 Agent 代表用户登录从两个维度改变了网络钓鱼的攻防逻辑:一方面,由于 Claude Duet 本身不持有任何凭据,因此攻击者无法向其钓取密码,任何隐藏指令都无法迫使它吐出它根本未曾掌握的秘密;另一方面,登录表单本身会成为潜在攻击目标,因为任何需要输入密码的界面都有可能被仿冒。因此,Claude Duet 的登录表单只会在应用内部、且仅在您主动发起的登录流程中出现。它绝不会以链接、短信、电子邮件或 claude.ai 以外的任何网站形式呈现。如果在其他任何地方出现貌似 Claude Duet 的索取密码界面,均为仿冒。
登录 Token
当 Claude Duet 在已连接的应用中工作时,它遵循我们的 Claude Managed Agents 架构设计,使凭据始终处于 Agent 工作环境之外。Agent 代表您使用的凭据(如关联服务的登录 Token)绝不会进入 Agent 运行的机器;取而代之的是一个凭据占位符,只有当外部代理(Proxy)发起真实请求时,才会将其替换为真实值。
浏览器
Claude Duet 中为您分配的浏览器运行在云端专属的独立虚拟机内,与模型本身以及 Agent 运行的云端计算机完全物理隔离。Agent 仅能通过一组固定的指令集来驱动浏览器:打开此页面、点击此处、在此输入。目标网站执行的任何代码均严格限制在浏览器虚拟机内。网站代码和 Cookie 既无法进入 Claude Duet 的记忆系统,也无法访问您已连接的应用,Agent 的任何指令也无法从浏览器中提取 Cookie。系统回传给 Agent 的仅包含页面文本和下载文件,因为 Agent 必须读取这些内容才能完成工作。这正是其他安全检查机制存在的意义,也是 Claude Duet 部署我们浏览器使用研究中详述的提示词注入防御方案的原因。Agent 经由浏览器上传的文件,也会接受与外发消息完全相同的敏感信息检查。
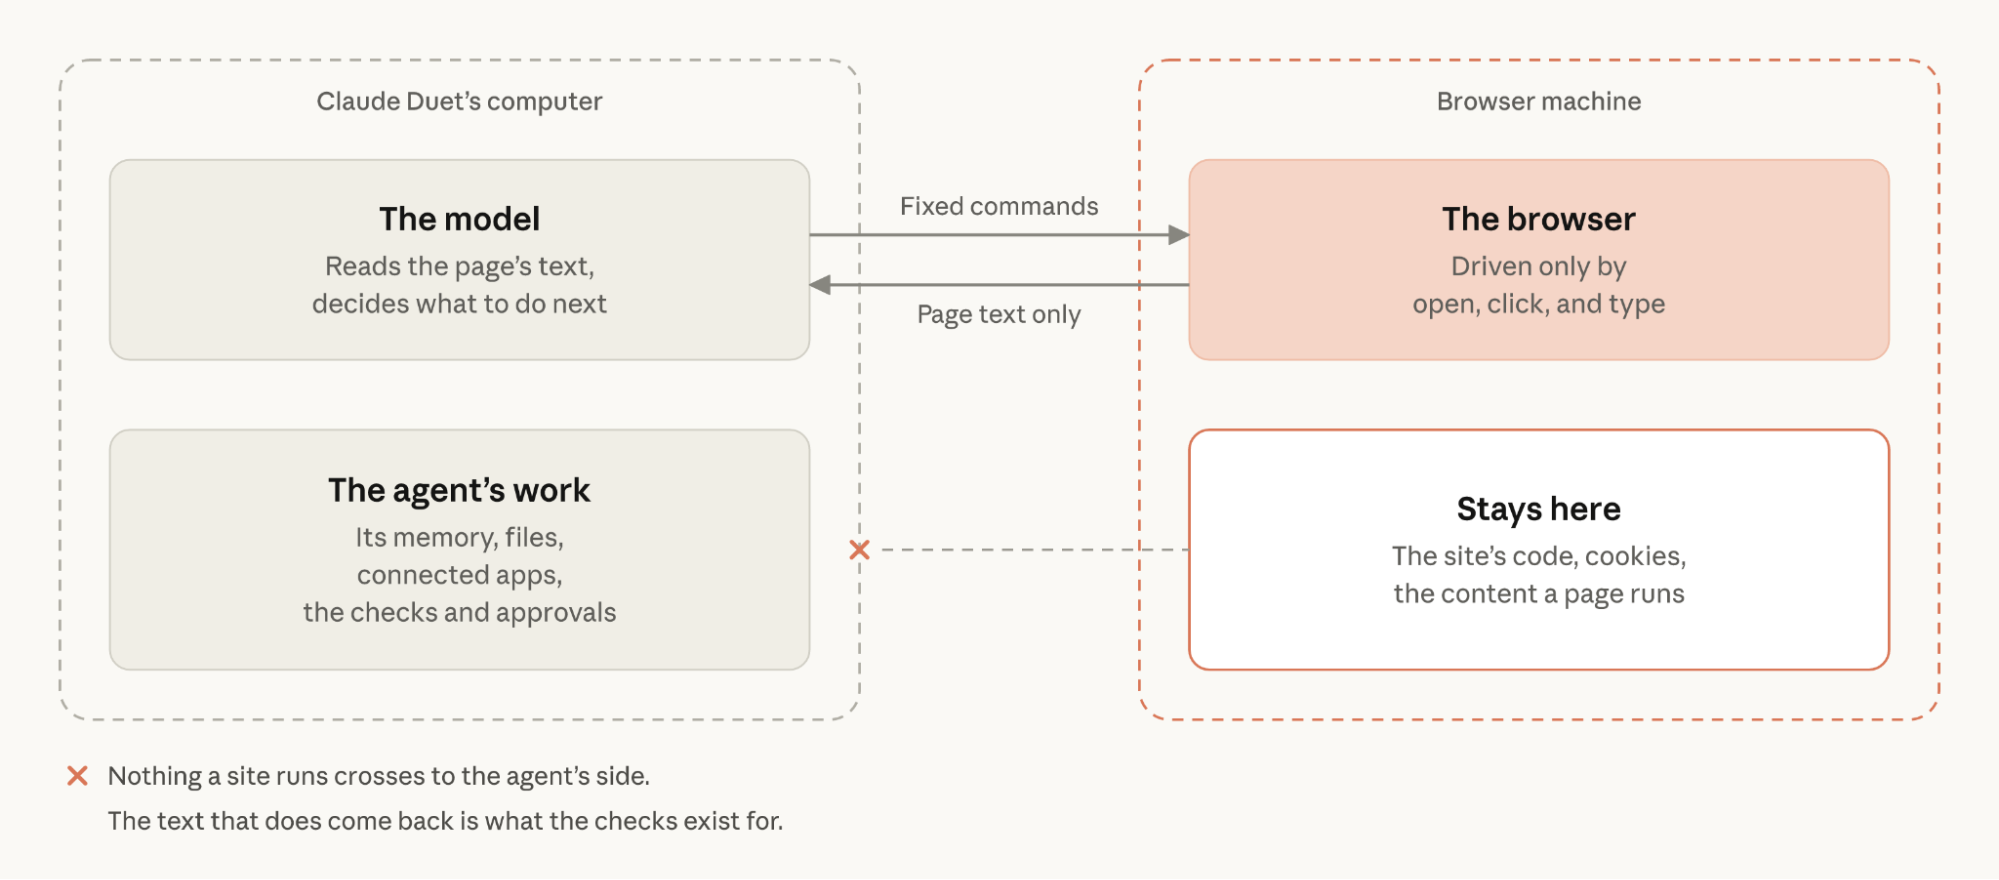 图 3. 浏览器边界:传输的仅限于固定指令,返回的仅限于页面文本,而网站的代码、Cookie 和下载内容均停留在浏览器虚拟机中。
此外,Claude Duet 还被设计为主动表明其 Agent 身份。目前,其 Web 浏览器发出的网络请求均包含明确的 User-Agent 标头,且我们公开了其浏览操作所使用的公网 IP 地址段,以便网站识别并自主决定处理策略。在产品发布前,我们主动联系了多家大型网站,并为它们提供了阻止 Claude Duet 访问的选项,部分网站选择启用了该限制。随着研究预览阶段的推进,我们将持续完善 Claude Duet 的身份标识机制。
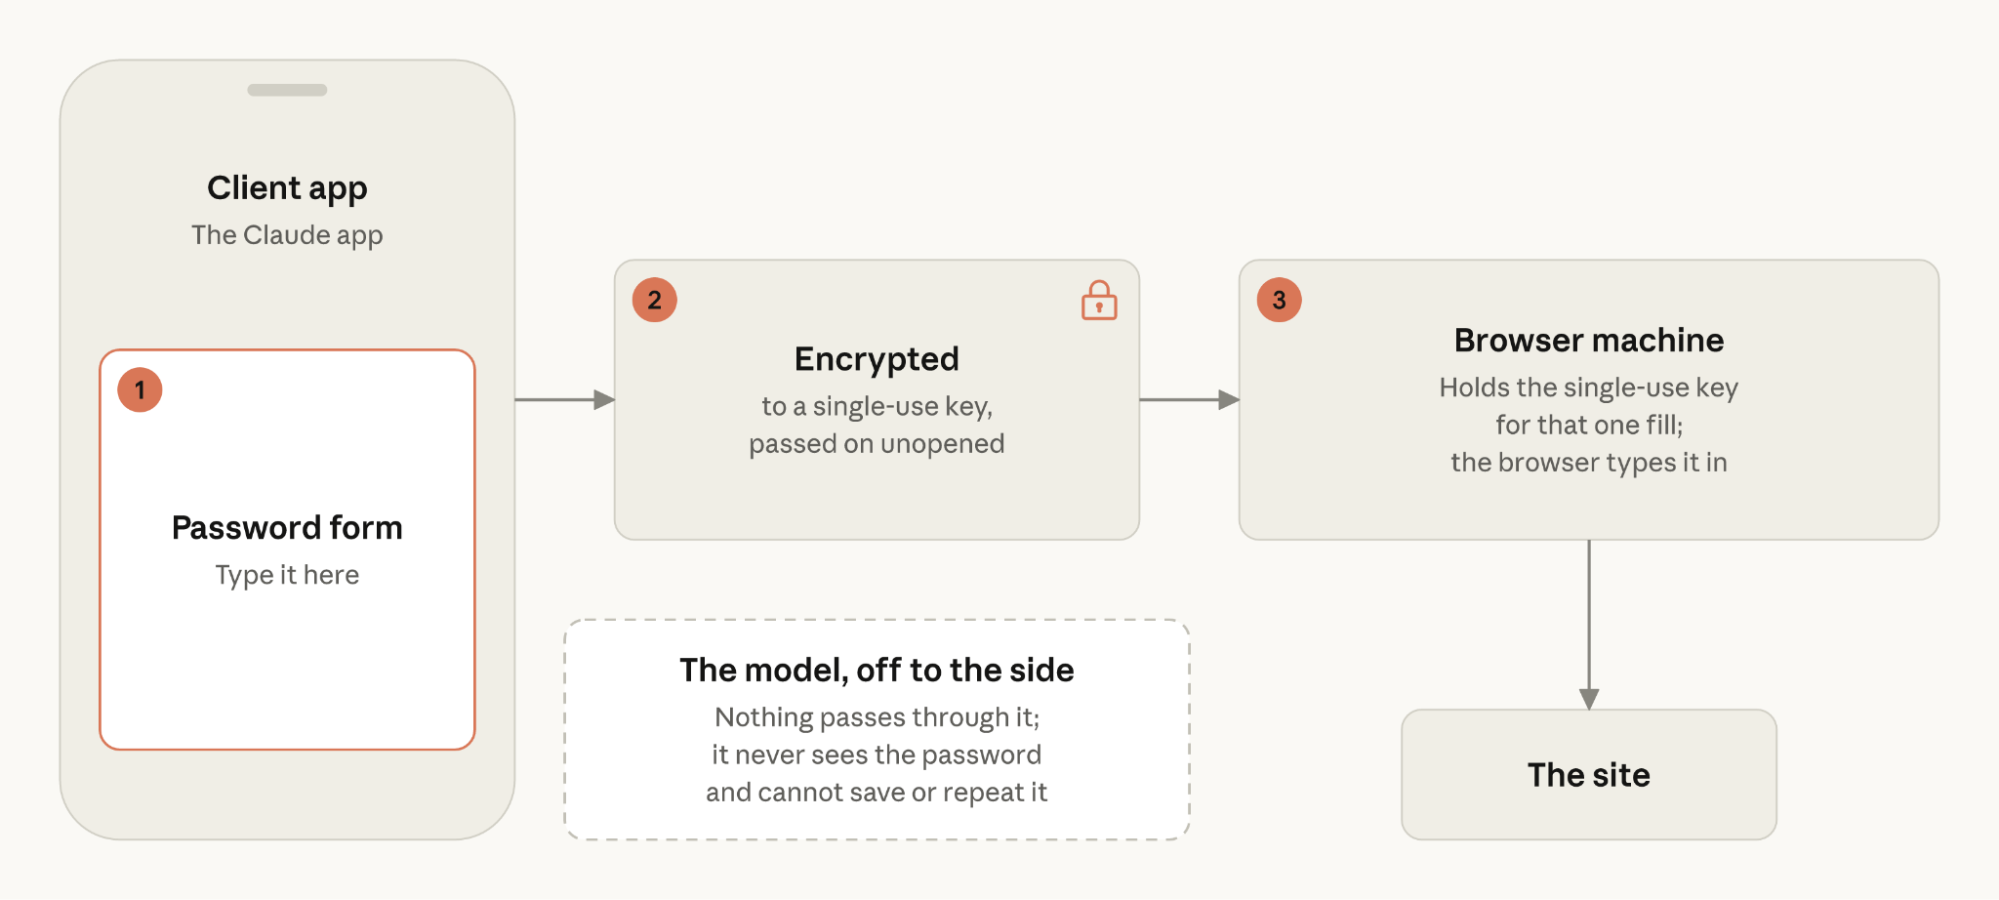 图 4. 凭据路径:密码在您的设备端完成加密,仅在浏览器虚拟机上解密,绝不经过模型本身。
我们如何对 Claude Duet 进行测试
安全测试在研究预览版上线前很久就已全面启动,且目前仍在持续进行中。我们的安全保障团队(Safeguards team)基于常见日常任务构建了评估基准,每个任务均派生为三种变体:正常良性版本、植入注入指令的版本,以及诱导 Agent 超出授权范围行动的版本。这些测试与来自真实使用场景的影子流量(Shadow Traffic)并行运行。
红蓝对抗团队进一步针对 Claude Duet 是否会发生信息泄露、未经审批擅自操作或遵循恶意提示词进行了深度红队测试。我们针对整个系统涉及的代码仓库和信任边界构建了全局威胁模型。一家外部渗透测试公司在获取我们源代码访问权限的前提下对 Claude Duet 进行了全方位测试,目前涵盖云端浏览器和登录表单的后续渗透评估正在进行中。每一项涉及凭据的新功能,在正式发布给任何用户之前,都必须在隔离环境中通过红队攻防测试。
Claude Duet 也已被正式纳入 Anthropic 的公开漏洞赏金计划。根据我们的负责任披露政策,该计划对有效的漏洞报告提供奖金,并为善意研究提供安全港保护。如果您发现了安全漏洞,欢迎通过我们在 HackerOne 上的 Anthropic 漏洞赏金项目进行提交。
与您共同构建
我们之所以将 Claude Duet 作为研究预览版发布,是为了深入了解用户对个人 Agent 的真正诉求,包括大家期望在未来看到的保护措施与控制选项。本文所介绍的部分机制目前仍在演进中:包括请求审批的频率阈值、登录交互方式,以及敏感信息检查区分私密数据与无害内容的精准度。您只需直接用自然语言告诉 Claude Duet 您的期望或遇到的问题,它便会自动向我们的团队提交反馈报告。
English / 原文
Claude Duet (opens in new tab) is an agent, currently in research preview, that uses a cloud-based computer to do work for you. It can use all the apps and services you've chosen to connect to Claude, and it runs continuously even after you close the app. It can read your inbox, draft replies, book things, and run routines while you are away. Our team runs Claude Duet on our own accounts and we use it for work every day.
We built Claude Duet on three principles to guide the agent's behavior:
- Your information, and what other people share in your connected apps, is handled with discretion, using a new classifier that checks messages Claude Duet drafts before they go out.
- You stay in control of what it does on your behalf.
- Claude Duet never sees your passwords, browser cookies, sign-in tokens, or other credentials.
Claude Duet is new but the thinking behind it is not. In 2025 we published our framework for safe and trustworthy agents (opens in new tab), which puts people in control and treats privacy and secure interactions as basic requirements. Since then, we have written about why no single defense is enough (opens in new tab) and why protection inside the model can’t stand alone (opens in new tab). We also build and operate the infrastructure businesses use to run agents in production through Claude Managed Agents (opens in new tab), and Claude Duet keeps credentials separate from the agent in the same way. It builds on this work, adding the protections that an agent acting for you needs. This post walks through what we added and what we’re still working on.
You approve important actions
An agent that acts while you’re away has to know when to stop and ask for permission before proceeding, and to do it at the right cadence. Before Claude Duet does something like sending a potentially sensitive message, paying for something, or deleting anything, it shows you the action, the destination, and the content, including every recipient. It then waits for you to approve the action.
A separate, automated check runs alongside each action, built on the auto mode classifier from Claude Code (opens in new tab) and extended for Claude Duet. It assesses whether the action matches your intent. The check runs outside the model doing the work so instructions hidden in a page cannot affect the outcome.
Some actions stay off-limits even with your approval, like trading securities, banking actions such as moving money between accounts, and accessing someone else's account. Some other steps aren’t covered by a "don't ask me again" rule, however often you have approved them, like paying or sending money, deleting an order, or creating an account. The routines that run while you are away have the same safeguards.
We spent a lot of time calibrating how often Claude Duet asks for approval. Approval fatigue is a serious issue, because too many requests teach people to tap through them, sometimes without adequate consideration. We will continue to adjust this calibration over time.
For purchases, Claude Duet pays with a one-time card from a wallet like Link from Stripe, limited to that merchant and amount. You see the item and the total, and you approve the purchase in your Link app. Your real card number isn’t shared with Claude Duet or the merchant.
Figure 1. Approval flow: the approval card and the separate check sit outside the model, so nothing the agent reads can answer the card.
Your information is handled with discretion
An agent that reads your email and sends messages for you is constantly deciding where different types of information should go. If you ask Claude Duet to send your team a weekly recap, it should include only things everyone on the team already has access to and never private details, like your performance review conversations.
To address this, we built a new safety classifier that runs separately from the main model and checks whether each message Claude Duet is about to send contains potentially sensitive information. We categorize this information into two tiers:
- Never share: We give the most sensitive protection to information like sign-in credentials, full card and bank account numbers, and government ID numbers. Claude Duet is instructed never to share these with anyone, even if you ask.
- Needs consent to share: Claude Duet will share other private information, such as health or finances, only if you’ve explicitly approved it. Your own request counts as consent, so “send a note to my dentist about my tooth pain” generally won’t need additional approval.
Figure 2. Where your information can go: before anything is sent, the check weighs how sensitive the information is and whether you’ve given consent.
If Claude Duet is blocked for either reason, it can decide to rewrite the message without the sensitive information and share with you for approval.
Claude Duet is still in research preview and these safeguards will occasionally miss something or flag a harmless message. That’s why they work alongside the approval mechanisms above, which are designed to keep you in control of what Claude Duet sends on your behalf. We expect to continue iterating on our classifier as we learn more about how people use Claude Duet.
You have visibility into tasks and connected apps
You can see what Claude Duet has done and is doing in its task list, where each task has its own page, and steer it mid-task. Claude Duet keeps your conversation history and its memory so it can carry context between tasks, until you delete your history or reset it. Deleting your account wipes everything Claude Duet has stored.
The apps you have connected to Claude carry over to Claude Duet, and switching an app off in one place switches it off in both. Disconnecting an app stops new access from that moment, but what Claude Duet already learned from it stays until you reset its memory, which you can do anytime from the app’s settings. Claude Duet also uses the memory from your Claude account, so details Claude remembered from your earlier chats are visible.
Credentials and the browser are isolated from the model
Claude Duet never sees your passwords, browser cookies, or the sign-in tokens for your connected apps, and it can’t save them to its memory. They only ever pass through separate machines the model can’t access, and the approvals and safety checks that govern what it does run there too.
Passwords
When a site asks for a password, you type it into a form inside the Claude app. The form encrypts it with a single-use key that exists only on our secure cloud browser machine, for that one single use. It passes the encrypted password unopened to the browser, which types it into the site. The model doesn’t see the password and can’t save or repeat it. Soon you will also be able to sign in with 1Password; Claude Duet will ask for a credential, you will approve that request in 1Password, and the credential will go to the browser without passing through the model.
An agent that signs in for you changes phishing in two ways. On one hand, Claude Duet doesn’t hold credentials for you so it can’t be phished for a password, and no hidden instruction can make it reveal a secret it doesn’t have. On the other hand, the sign-in form is itself a target, because anything that asks for a password can be imitated. So Claude Duet’s sign-in form only appears inside the app, during a sign-in you asked for. It never arrives as a link, a text message, an email, or a website other than claude.ai. If something that looks like Claude Duet asks for your password anywhere else, it’s not legitimate.
Sign-in tokens
When Claude Duet works in a connected app, it follows our Claude Managed Agents design (opens in new tab) so credentials stay out of reach of the agent’s work. Credentials that the agent uses on your behalf, such as a sign-in token for a connected service, never enter the machine where the agent works. A placeholder for the credential sits there instead and a proxy outside that machine puts in the real value only as a request is made.
The browser
Your browser in Claude Duet runs in its own dedicated virtual machine in the cloud, separate from the model and from the cloud computers the agent works on. The agent drives the browser only through a fixed set of commands: open this page, click here, type this. Whatever a site runs stays on the browser machine (opens in new tab). The site’s code and cookies don’t reach Claude Duet’s memory or your connected apps, and none of the agent’s commands can read cookies out of the browser. What does come back is the page's text and downloads, because the agent has to read them to do its job. That’s why the other checks exist, and why Claude Duet also uses the prompt-injection safeguards described in our browser-use research (opens in new tab). Files it uploads through the browser get the same sensitive-information check as its messages.
Figure 3. The browser boundary: fixed commands go across, page text comes back, and the site's code, cookies, and downloads stay on the browser machine.
Claude Duet is also designed to identify itself as an agent. Today, requests that its web browser sends include a distinct User-Agent header, and we publish the public IP addresses it browses from, so sites can recognize it and decide how to treat it. Before launch, we also contacted several large websites and gave them the option to prevent Claude Duet from visiting their sites, and some chose to. We’ll keep refining how Claude Duet identifies itself as we learn from the research preview.
Figure 4. Credential path: the password is encrypted on your phone, opened only on the browser machine, and never passes through the model.
How we tested Claude Duet
Testing started well before the research preview and continues now. Our Safeguards team built evaluations from routine-shaped tasks, each in three variants: an innocent version, one with injected instructions, and one that tempts the agent to do more than it was asked. Those run alongside shadow traffic from real use.
Red teams further tested whether Claude Duet would leak information, act without approval, or follow malicious prompts. We built a threat model of the whole system, across the repositories and trust boundaries it touches. An external penetration-testing firm tested Claude Duet with access to our source code, and a follow-on engagement covering the cloud browser and the sign-in form is running now. Each new credential feature is red-teamed on an isolated rig before it ships to anyone.
Claude Duet is also in scope of Anthropic’s public bug bounty program, which rewards valid reports and offers safe harbor for good-faith research, under our responsible disclosure policy. If you find a security vulnerability, we want to hear about it: report it through Anthropic’s bug bounty program on HackerOne (opens in new tab).
Building this with you
We’re releasing Claude Duet as a research preview because we want to learn what you value in a personal agent, including the protections and controls you’d like to see next. Some of what’s described here is still changing: how often it asks for approval, how you sign in, and how well the sensitive-information checks tell what’s private from what’s harmless. Tell Claude Duet in plain words what you’d like to see or what went wrong, and it will file a report for our team.